Agent MCP vs Tool MCP: Pick Before You Connect
This week AlphaSense, MindBridge, Tracebit and Brightcove shipped MCP servers, while Glow Labs flagged agents installing deprecated reference packages. Here is how to tell tool MCPs from agent MCPs before you connect.
Overview
This week vendors stopped treating MCP as a thin API wrapper. On November 4, 2026, AlphaSense launched SuperAnalyst MCP, a research agent you delegate objectives to, not a pile of search tools. A day earlier, MindBridge shipped a read-only MCP for financial risk investigation inside Claude, Copilot, and Cursor. Tracebit and Brightcove published MCP servers the same week for deception ops and video workflows.
In parallel, Glow Labs described MCPhantom: coding agents installing archived Anthropic reference MCP packages from training memory, including an unpatched prompt-injection path to RCE in the old Puppeteer server. So the catalog is growing fast, and so is the cost of connecting the wrong server.
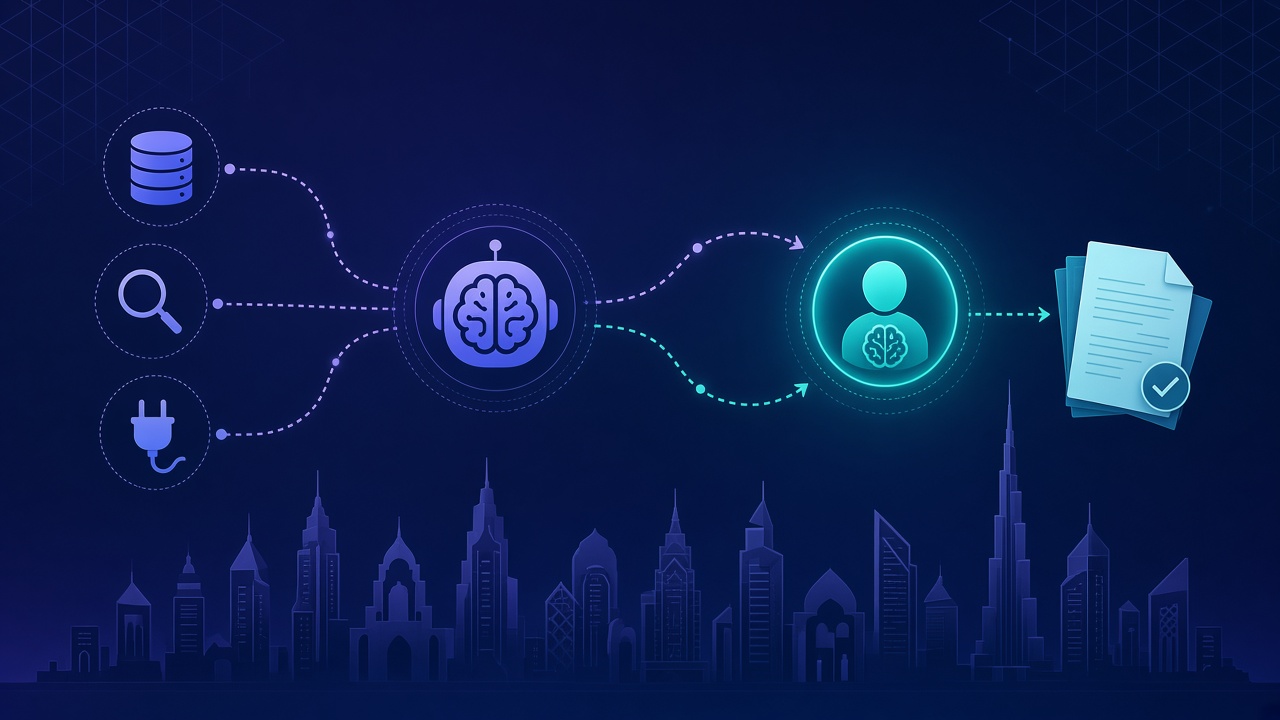
Treat every new MCP as either a tool catalog or a specialist agent. Mixing those two without an allowlist is how context, cost, and risk blow up.
Two kinds of MCP, one protocol
| Kind | What you get | Example this week | Your job |
|---|---|---|---|
| Tool MCP | Schemas and actions your agent calls step by step | MindBridge analysis lookup; Brightcove media APIs | Plan, call, reconcile results in your harness |
| Agent MCP | An objective in, cited work product out | AlphaSense SuperAnalyst MCP | Decide when to delegate; keep firm context on your side |
AlphaSense's post is blunt about the tool-MCP tax. Each vendor MCP adds tool definitions to the model context before work starts. Agents stop picking the right tool once the list gets long. When every MCP only retrieves, your harness still does research planning, conflict resolution, and "enough evidence" checks. On a typical multi-hop research loop, most of the token bill is context the model already saw.
An agent MCP flips that. Your orchestrator keeps CRM notes, house views, and policy. The specialist MCP plans research, weights sources, and returns an answer, workbook, or evidence pack with citations. You still own the decision. You stop paying your frontier model to rediscover the vendor's domain.
MindBridge sits closer to a governed tool MCP: find analyses, explore risk fields, explain control points, query high-risk transactions. It is read-only, off by default, and gated by the authenticated user's existing permissions. That is the pattern finance teams should insist on for any MCP that can see ledgers.
What changed this week (with sources)
- AlphaSense SuperAnalyst MCP (4 Nov 2026). One MCP over filings, transcripts, expert calls, models, and more; built as a research agent with citations. AlphaSense reports roughly 3x lower cost per correct answer versus a frontier model doing raw retrieval over the same content, and preference more than 2:1 in their tests. Treat those as vendor figures until you reproduce them on your prompts.
- MindBridge MCP (3 Nov 2026, release 26.10). Natural-language investigation of completed risk analyses inside assistants your auditors already use. Admin enablement plus risk disclosure required.
- Tracebit MCP (4 Nov 2026). Agents can create artifacts, deploy canaries, triage alerts, and pull posture reports. Write actions are in scope, so treat it like production ops access.
- Brightcove MCP (3 Nov 2026). Video platform capabilities inside existing AI workflows instead of forcing operators into the Brightcove UI.
- MCPhantom (reported ~2 Nov 2026). Glow Labs found agents choosing deprecated
@modelcontextprotocol/server-*packages from training data in 98% of the sessions where a deprecated server was installed. Four high-severity issues in archived reference servers; Puppeteer has a prompt-injection-to-RCE path. Maintainers say those archived servers will not be patched.
Yesterday we covered Amazon Connect Customer calling MCP tools from flows. Same protocol, different consumer. This week's launches are about which servers you trust on the other end of that wire.
How to choose before you connect
1. Label the MCP: tool or agent
If the vendor asks you to "delegate an objective," it is an agent MCP. If it exposes find/query/create tools and leaves planning to you, it is a tool MCP. Put that label in the allowlist entry. Your orchestrator policy should differ: agent MCPs get fewer sibling tools; tool MCPs get tight schemas and timeouts.
2. Prefer the service owner's server
MCPhantom exists because models remember early Anthropic reference package names. For GitHub, CRM, finance, or video, approve the current server the service publishes, not an npm package an agent invents from memory. Write the exact package or URL in AGENTS.md / Claude settings / your gateway config.
3. Cap how many tool MCPs sit in one agent
AlphaSense's warning matches what we see in production agent stacks: too many MCP tool lists in one session and the model thrash-calls or skips. Group tools behind one product-owned gateway (same idea as our earlier MCP gateway guidance), or replace a cluster of retrieval MCPs with one specialist agent MCP when the domain is research-heavy.
4. Match permissions to write risk
MindBridge's read-only, admin-off default is the bar for anything that touches financial or personal data. Tracebit-style write MCPs need the same change control you use for production consoles: named owners, audit logs, and no "developer laptop only" installs for shared agents.
5. Ban archived reference servers on every machine
Inventory MCP configs for archived @modelcontextprotocol/server-* packages, especially Puppeteer. Use denylists (deniedMcpServers in Claude Code, org MCP allowlists in Cursor Enterprise) so agents cannot reinstall them from training memory. SCA will not see npx installs that never land in a lockfile.
A practical week for a Gulf product team
- List every MCP your agents and IDEs already load. Mark each tool vs agent, owner, read/write, and last verified package or URL.
- Remove or replace any archived Anthropic reference server. Prefer the vendor's current MCP.
- For research-heavy work (competitive intel, investment memos, supply-chain briefs), trial one agent MCP such as SuperAnalyst on a closed prompt set and measure cost per accepted answer yourself.
- For audit and finance assistants, only enable MCPs that are read-only by default and inherit user permissions, MindBridge-style.
- Keep product actions (POS lookup, WhatsApp ops, ticket create) on your own catalog behind one gateway so Connect flows, chat agents, and IDE agents do not each invent wrappers. That is the same catalog pattern we use on products like AgentsCreator and WhatsApp POS.
When this fits (and when it does not)
Fits when you already run agents or IDE assistants against SaaS data, you are drowning in per-vendor tool MCPs, or security just asked what MCP packages developers installed via npx.
Wait when you still lack an allowlist, when a vendor MCP requires write access you have not risk-reviewed, or when you have not decided which model owns firm-specific context. An agent MCP does not replace your CRM notes or policy engine. It replaces the research loop you should not rebuild for every vendor.
Where we would help
We design MCP catalogs, gateways, and agent products so UAE and Gulf teams can adopt vendor MCPs without cloning every tool into a one-off Lambda. If you want a governed tool list for contact center and WhatsApp agents, or a clean split between specialist agent MCPs and your own actions, start from our AI integration services or tell us which servers are already in your configs.
Topics
Build this into a product
Talk to NTechnologies about applying these ideas in your stack.